FIREWALL MIGRATION
FIREWALL
MIGRATION
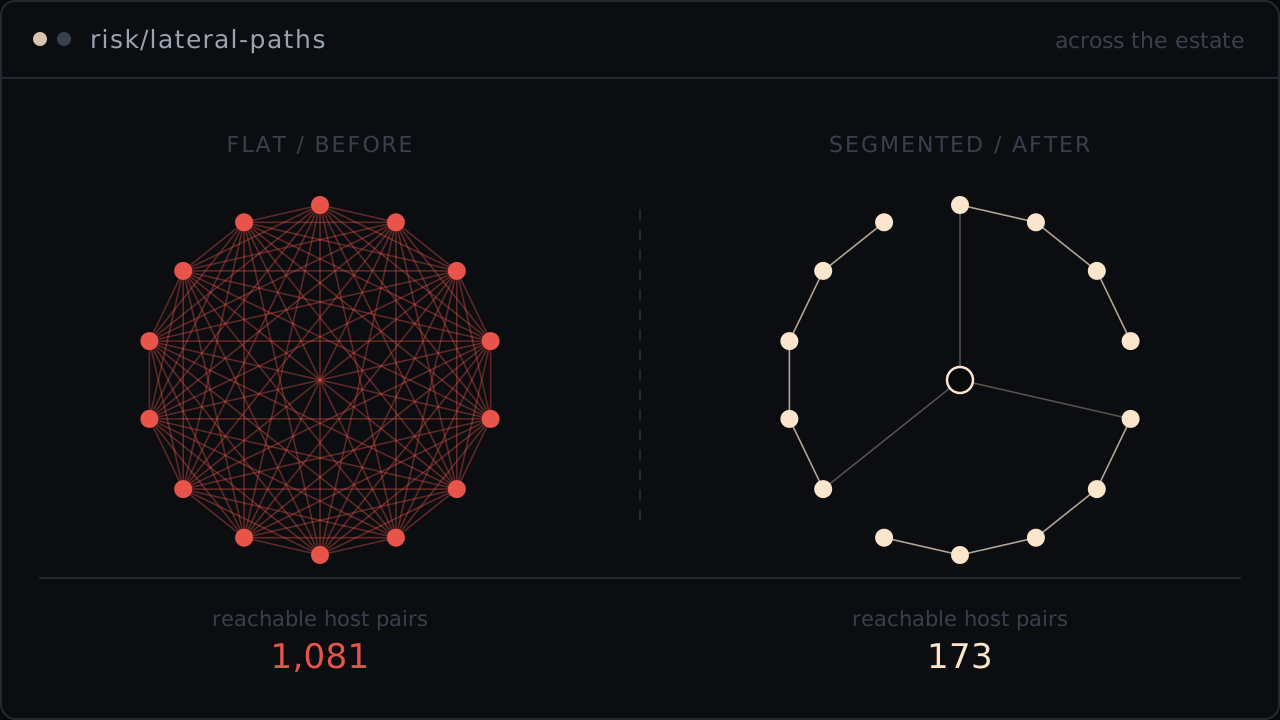
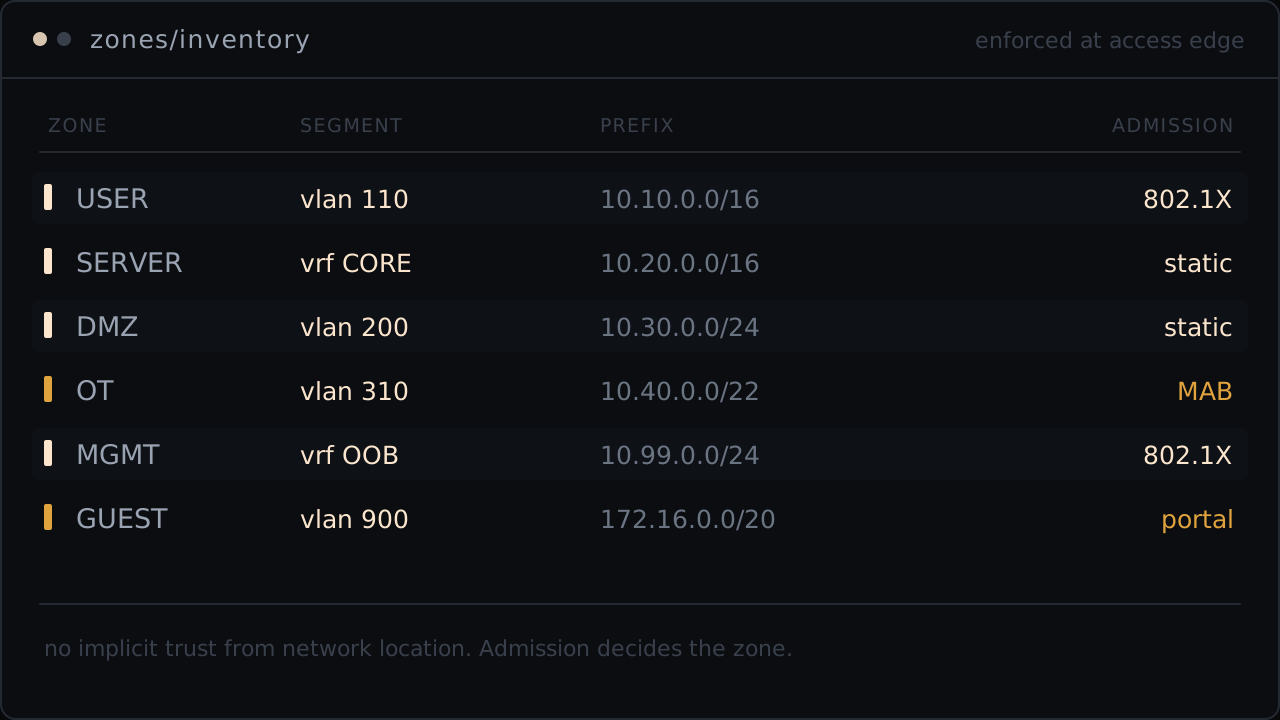
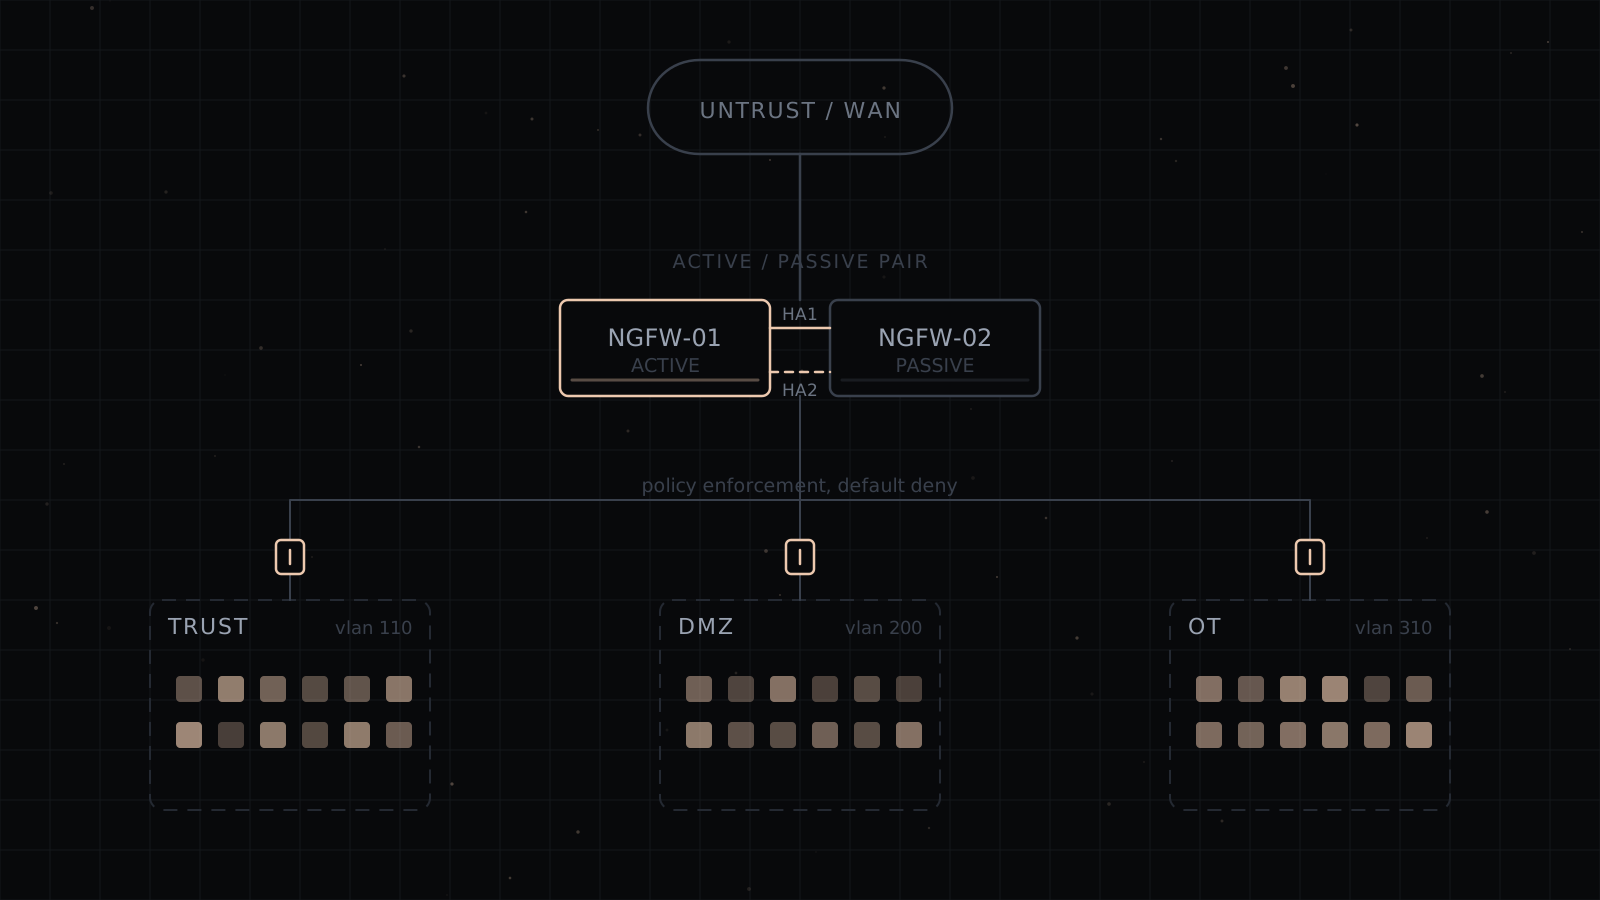
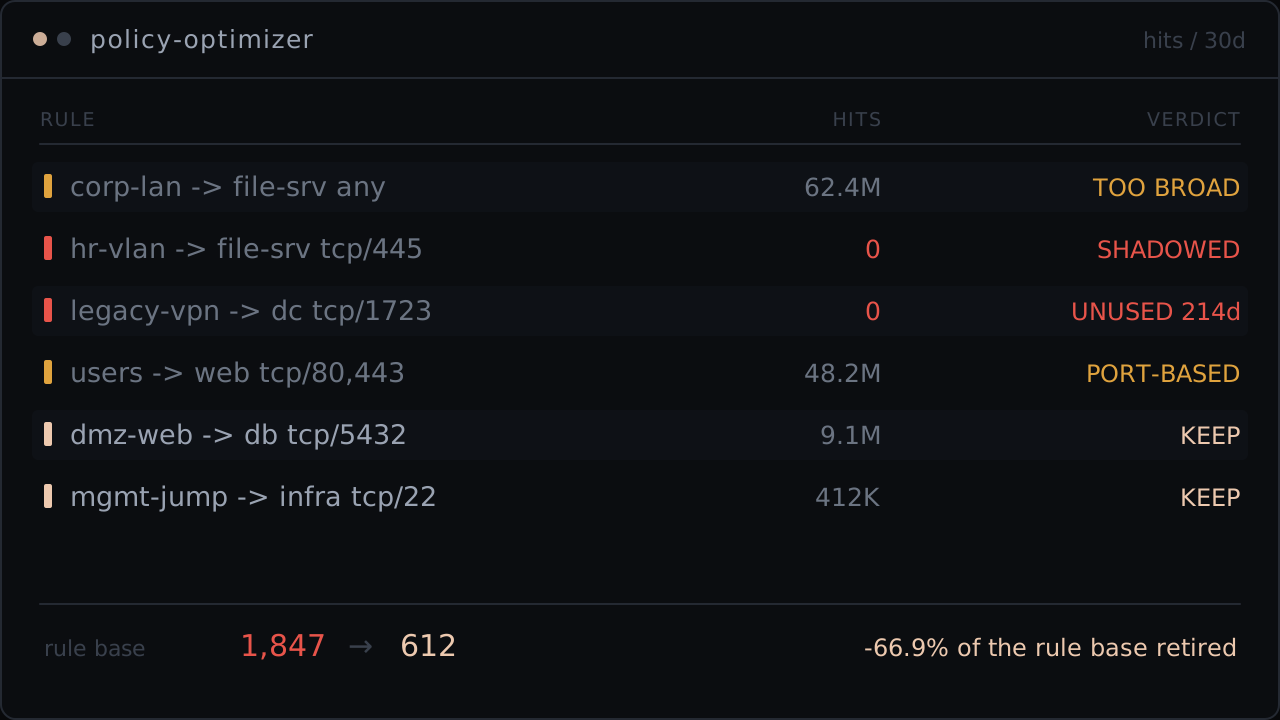
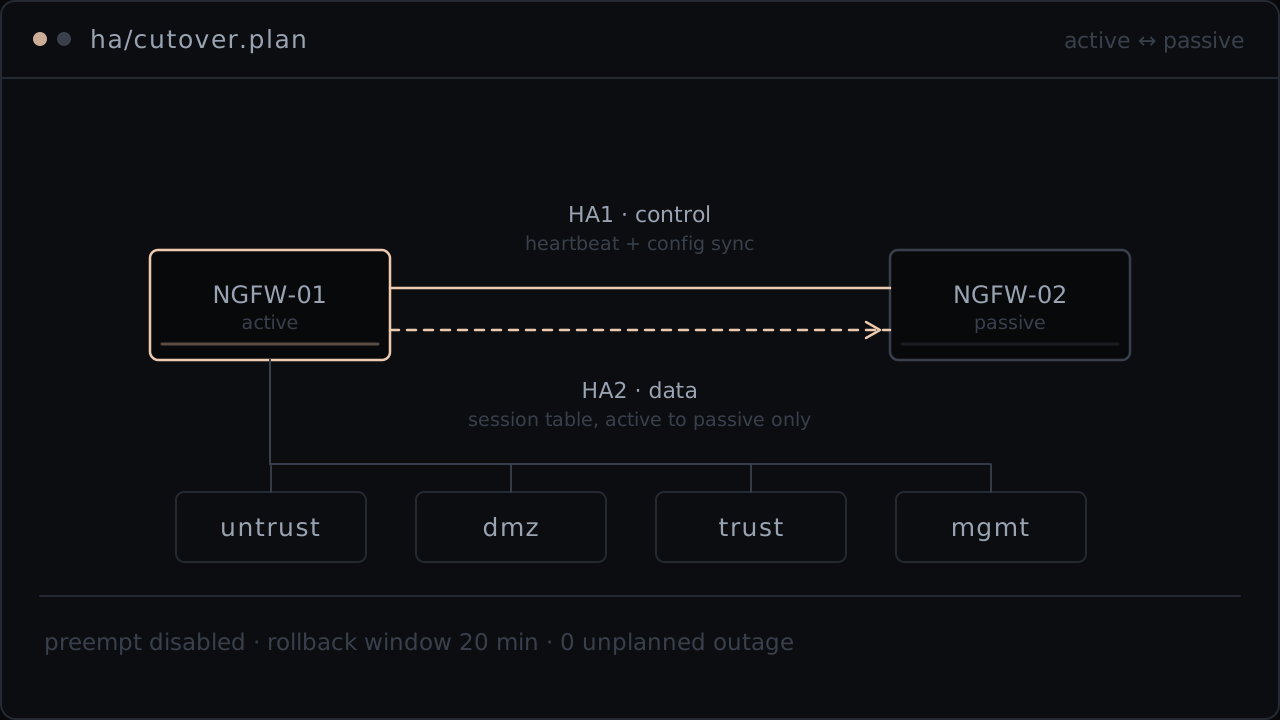
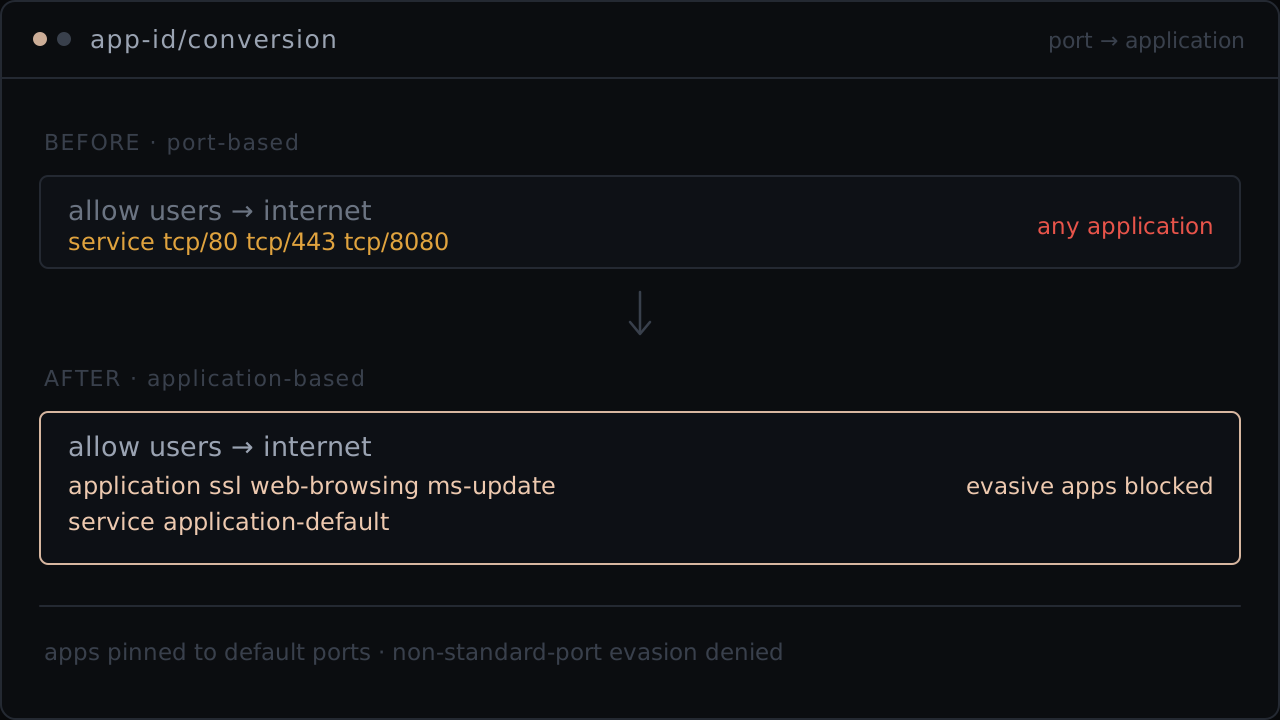
Perimeter at end of support, rule base unaudited for years. Rebuilt the policy from hit counts, dropped the dead rules, converted the rest to App-ID, then cut over to an HA pair.
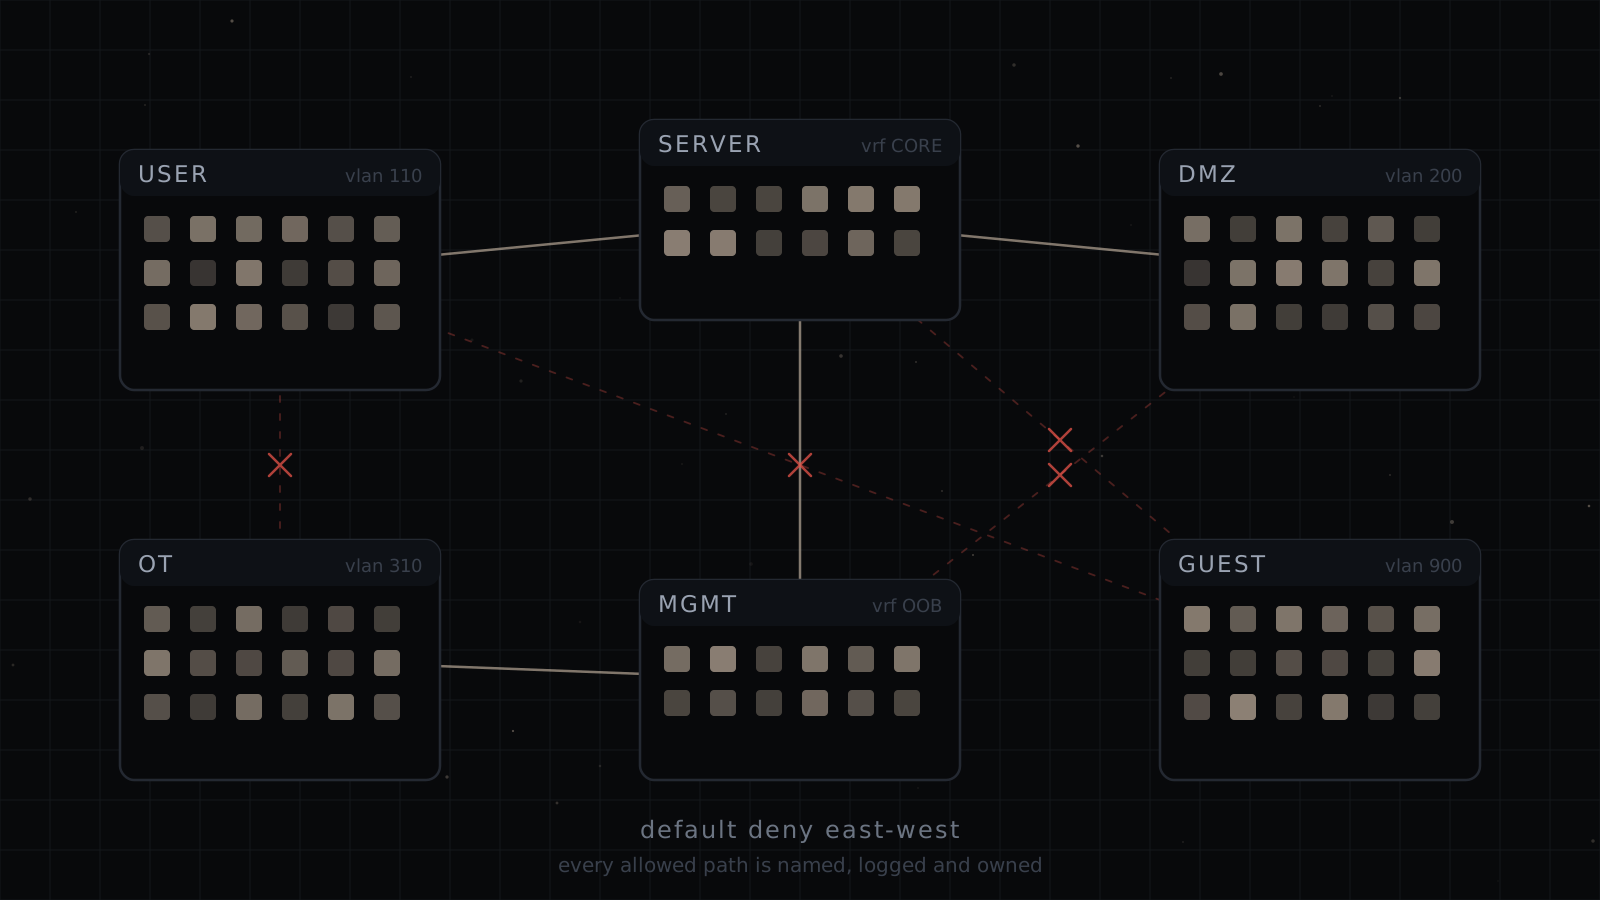
These are the properties I design for. A network that only works on a good day isn't finished, so the failure modes get mapped before they happen rather than explained afterwards. Meticulous is the difference between a firewall policy that passes an audit and one that passes traffic it shouldn't. Default is deny, and every exception has a name attached to it. Whoever inherits the estate can read what I changed and why, without calling me first. I like the work at the edges: the asymmetric route, the legacy rule everyone is afraid to delete. Most incidents I get called into were not clever attacks. They were something ordinary that nobody had thought to write down.
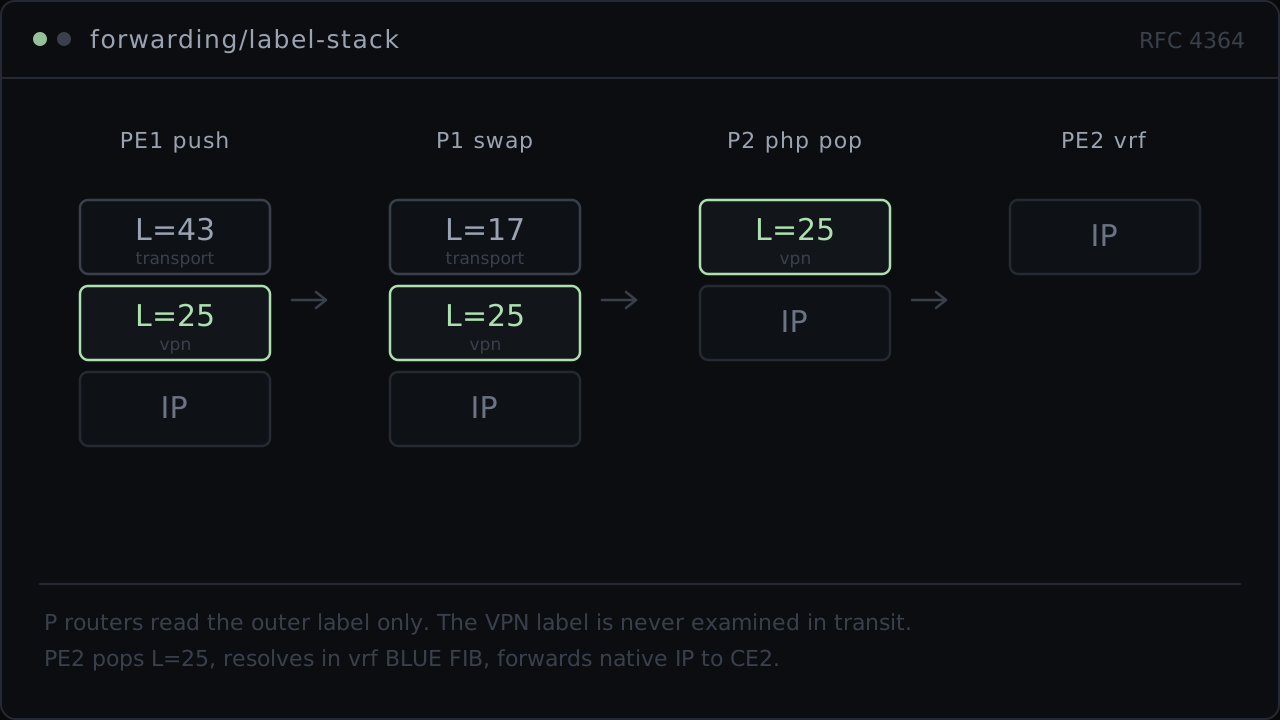
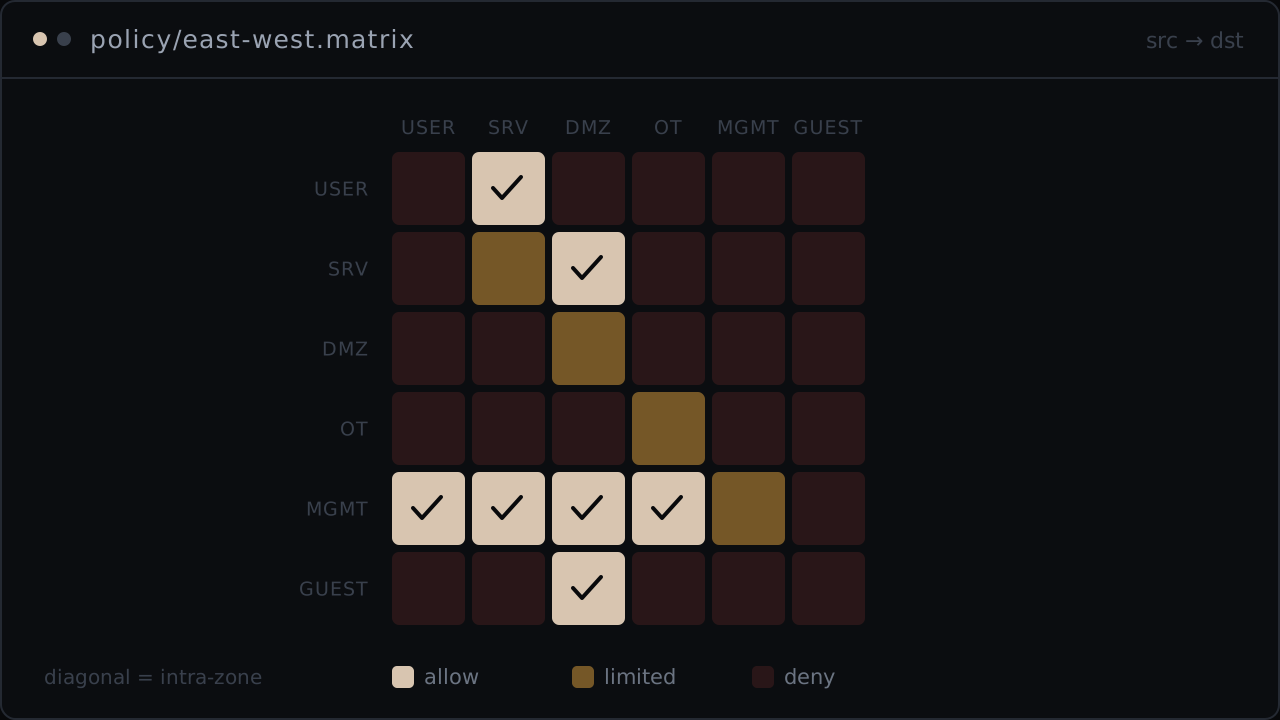
Network and security consultant, nine years in production infrastructure. Next-generation firewalls, MPLS L3 VPN and BGP design, segmentation and business continuity, from the first audit through to cutover. I also write the tooling that runs alongside it, mostly scanners and config management. Knowing how the applications on a network are built changes how you defend it.
Network and Security Engineer
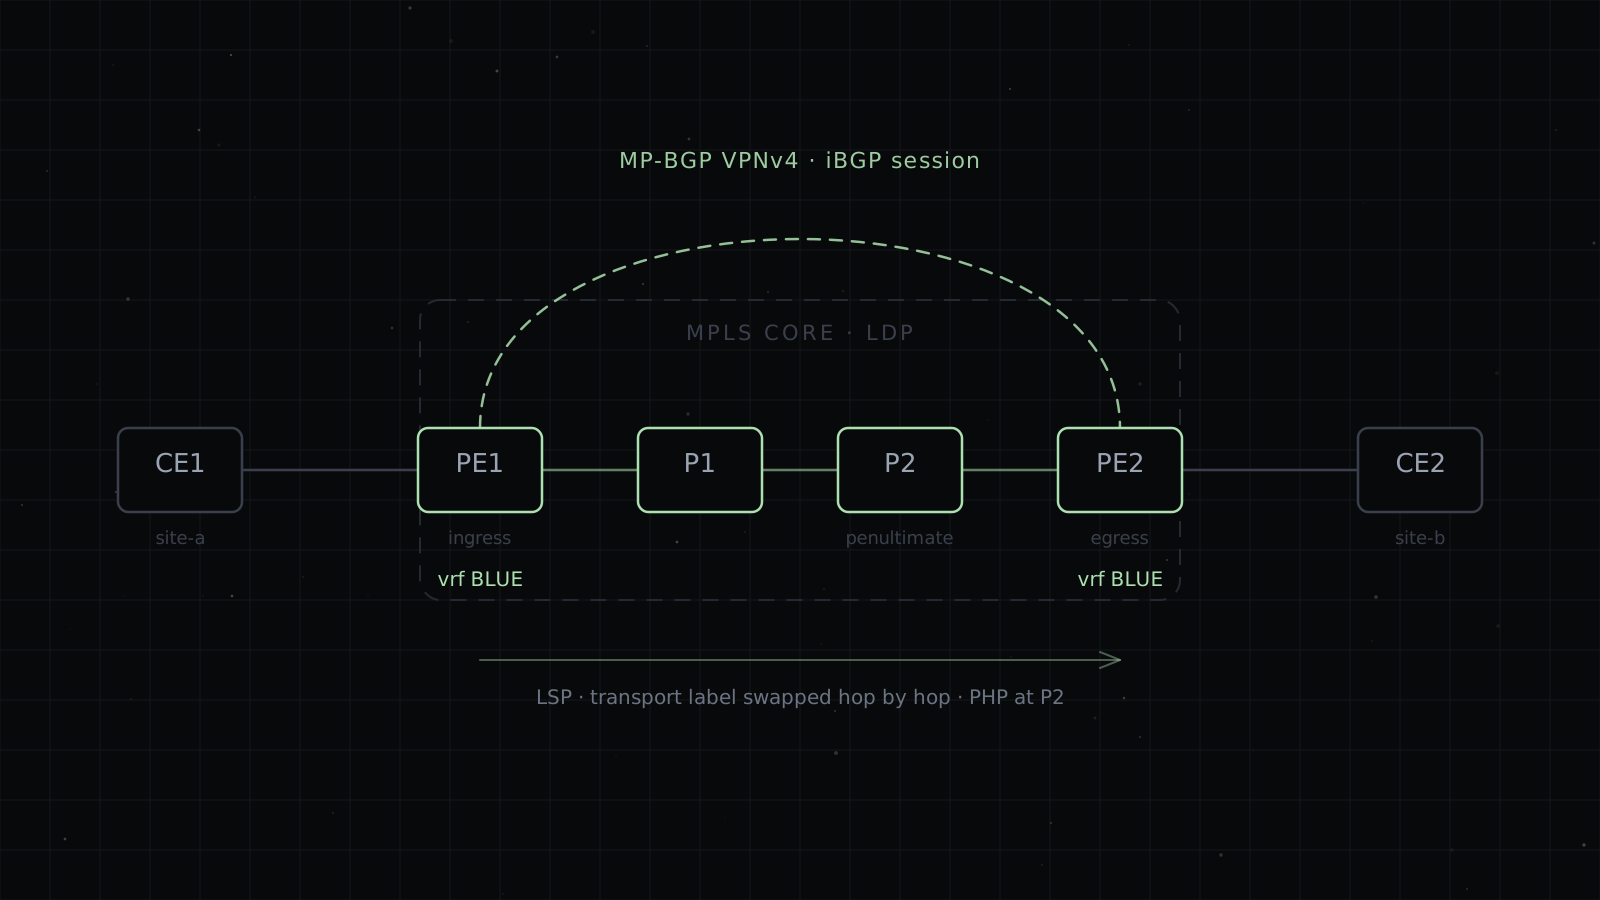
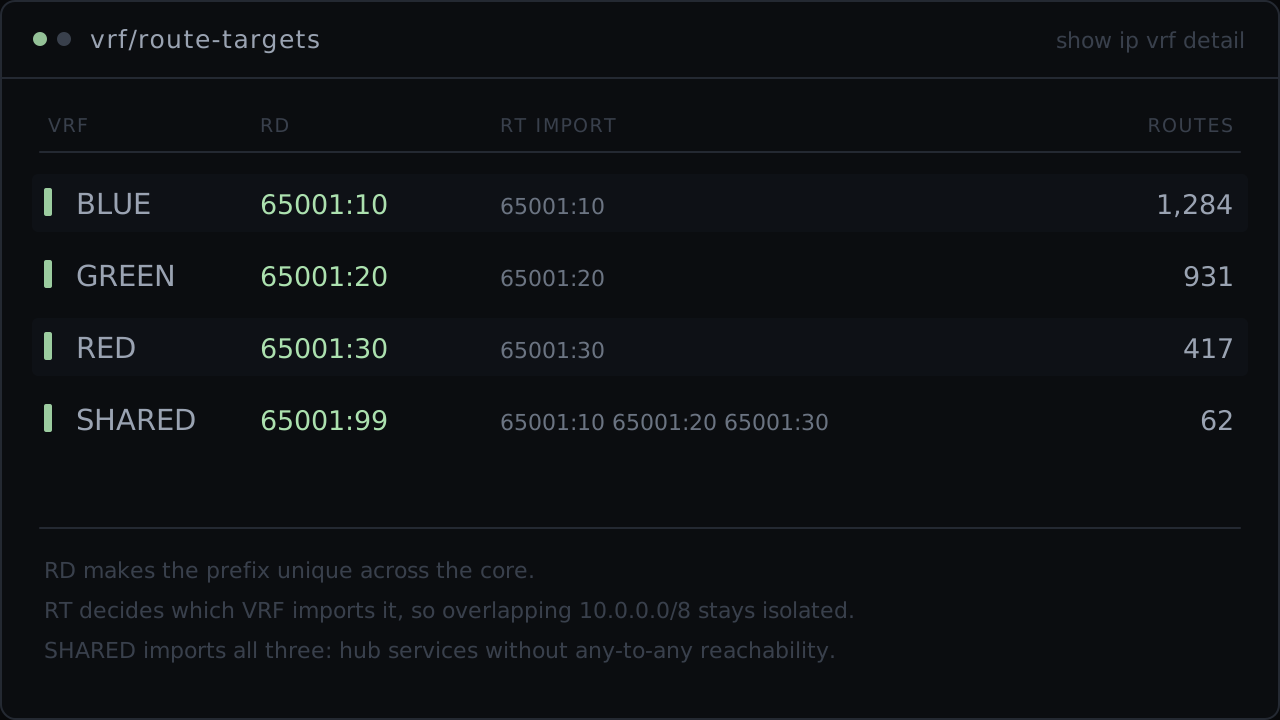
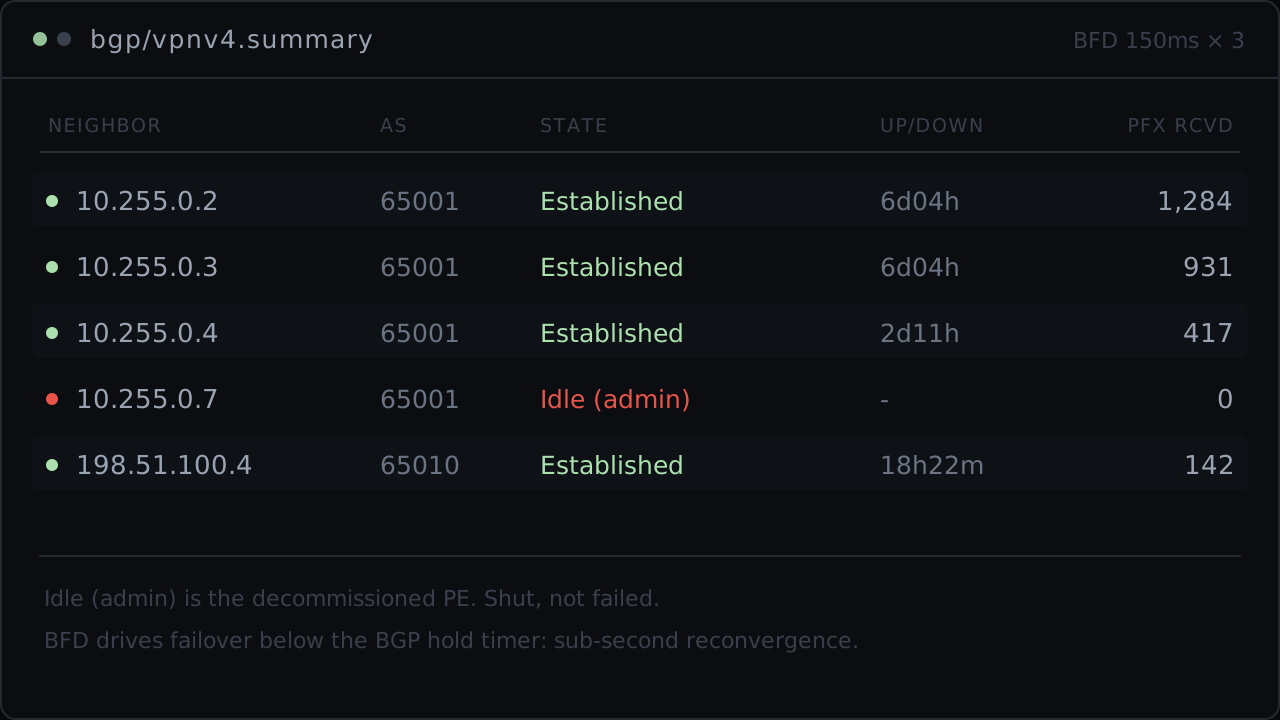
Architect, secure, and manage scalable network infrastructures, specializing in next-generation firewall deployment, proactive business continuity, and the end-to-end integration of complex MPLS L3 VPNs and BGP peering.
Senior Voice and Security Engineer
Architect and defend large-scale IP infrastructures through advanced firewall configuration, proactive vulnerability management, and the seamless integration of cross-platform security controls.
Full Stack Developer
Building the tooling side of the practice: secure APIs, hardened deployments, and custom automation for scanning, reporting, and configuration management, owning the full lifecycle from planning to production.
NOC Engineer
Secured and optimized global network footprints by managing the end-to-end administration of Windows/Linux servers and resolving high-tier L2/L3 infrastructure incidents.